TLDR
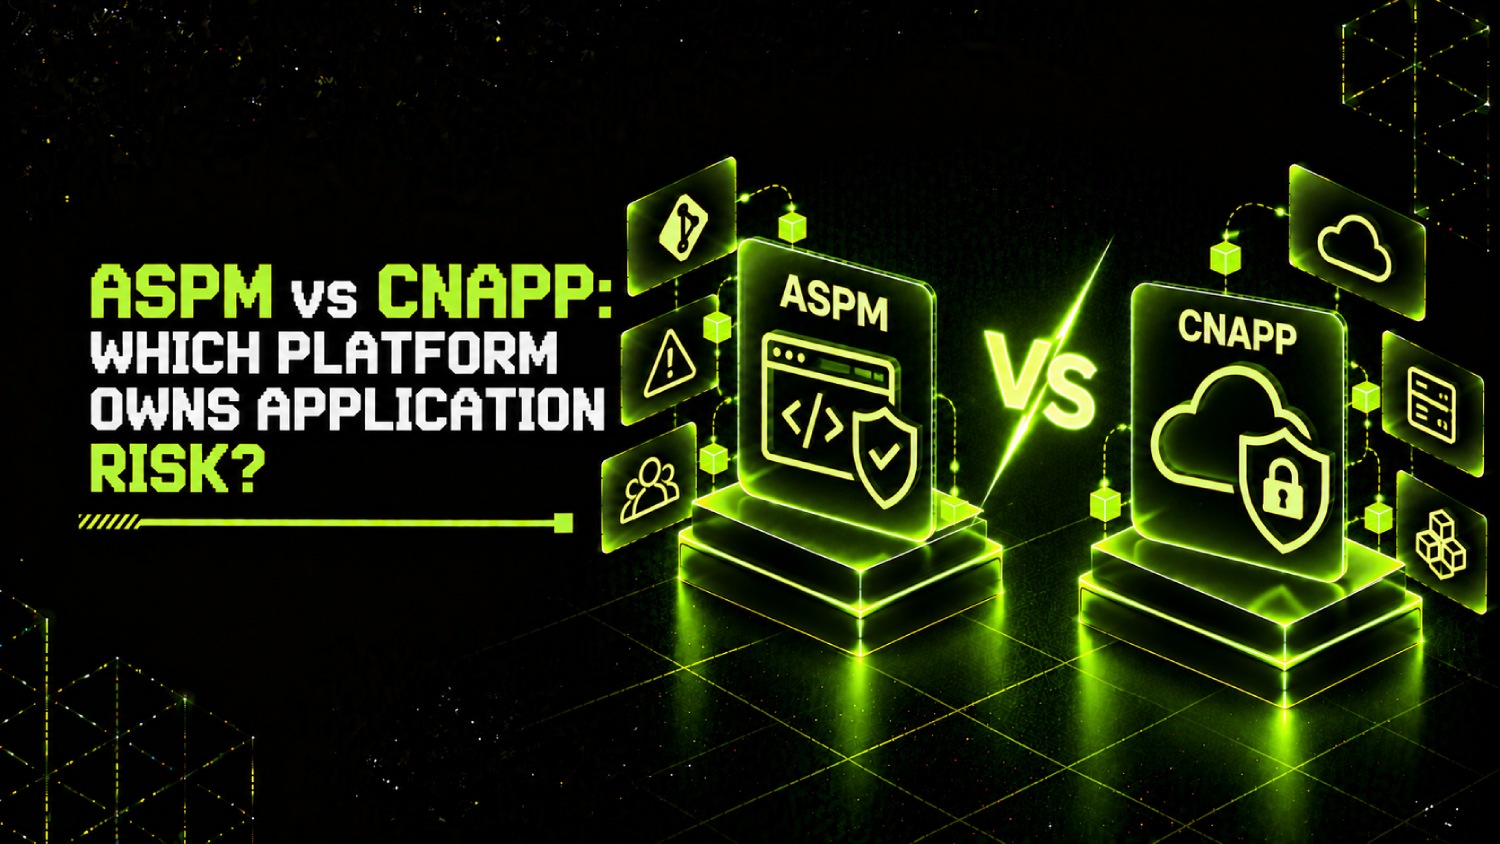
- CNAPP platforms own the runtime and infrastructure view of application risk: cloud configuration, workload posture, container drift, and attack path from deployed artifact back to blast radius. They do not own the code.
- ASPM platforms own the developer-side view: correlating scanner output across SAST, DAST, SCA, and secrets tools, routing findings to the right engineering team, and tracking remediation through the CI/CD pipeline. They do not own runtime telemetry.
- Both Wiz and Palo Alto Networks have made acquisitions to close the remediation-routing and pipeline security gaps in their respective CNAPP platforms. Both acquisitions signal that neither side had complete coverage independently.
- Consolidating appsec into your CNAPP almost always costs depth in developer workflow integration and scanner breadth. That trade is sometimes worth it. It should not be a surprise when it shows up six months post-contract.
- The coverage-gap checklist below is the decision tool neither vendor will hand you.
ASPM and CNAPP platforms address fundamentally different slices of application risk. CNAPP owns the deployed, running environment: misconfigurations, workload vulnerabilities, container posture, and the path an attacker walks from a public endpoint to a sensitive data store. ASPM owns the pre-deployment pipeline: aggregating findings from multiple scanners, correlating them into developer-routable tickets, and tracking fix velocity across engineering teams. Teams that consolidate all appsec into the CNAPP get unified billing and fewer vendor relationships, but typically lose scanner flexibility and the developer-workflow depth that dedicated ASPM tools provide. Teams running a standalone ASPM without CNAPP lose runtime context and cloud infrastructure correlation.
What Does CNAPP Actually Cover on the Application Security Side?
CNAPP, a category Gartner named, bundles CSPM, CWPP, CIEM, and increasingly code-pipeline scanning into one platform. The phrase “code to cloud” is common in CNAPP marketing. The runtime half of that phrase is accurate. The “code” half ranges from credible to aspirational depending on the vendor.
What most CNAPP platforms do well on the application security side: they know what code is actually deployed. They can see the container image, its base layer CVEs, whether the workload is internet-exposed, whether it has overprivileged IAM permissions, and what lateral movement paths exist from that workload to other services. That runtime context is genuinely useful for prioritizing which vulnerabilities matter. A critical CVE in a library that is deployed in an air-gapped, non-internet-facing pod is a different risk from the same CVE in a public-facing API with write access to your primary database.
Where CNAPP application security coverage gets thin: anything before the artifact reaches a registry. Most CNAPP platforms have added a CI/CD pipeline integration, often by acquiring one. Palo Alto Networks acquired Cider Security to bring supply-chain and pipeline security into Prisma Cloud, as described in its acquisition announcement. Wiz acquired Dazz to close the remediation-routing and risk correlation gap, as described in its announcement post. Both acquisitions are telling: neither platform had that capability organically, and integration into the core product takes time after an acquisition closes.
What Does ASPM Actually Cover That CNAPP Does Not?
Application Security Posture Management (ASPM) is a category built around one problem that CNAPP does not solve well: you have five or six security scanners producing findings, and no consistent way to deduplicate them, prioritize across them, and get the right finding to the right developer with enough context to fix it without a Jira-to-Slack-to-email chain. Vendors like Cycode, ArmorCode, and Ox Security built their platforms around this orchestration and normalization layer.
ASPM platforms typically connect to your existing SAST tools (Semgrep, Checkmarx, Veracode, Snyk), your SCA scanners, your DAST tools, your secrets scanners, and your CI/CD systems. They normalize findings into a common schema, apply reachability analysis and business context to prioritize, and route findings to engineering owners based on code ownership maps. That last part, knowing which team owns which service and routing accordingly, is where ASPM earns its keep in large engineering organizations where security cannot manually triage every finding.
What ASPM platforms generally lack: runtime cloud context. An ASPM tool knows a vulnerability exists in a library used by a service. It may not know whether that service is actually deployed in production, whether it is internet-facing, or whether the execution path that triggers the vulnerable code is ever actually called. That context lives in the CNAPP. Without it, ASPM prioritization relies on static reachability analysis, which is useful but incomplete compared to a platform that can see live workload traffic and configuration.
For security teams evaluating how ASPM fits into a broader application vulnerability program, the distinctions between ASPM and individual scanner tools like SAST matter more than most consolidation conversations acknowledge.
The Acquisition Signal: Why Both Sides Are Building Toward the Middle
The Wiz-Dazz and Palo Alto-Cider acquisitions are the clearest market signal available on where the category gap sits. Both CNAPP vendors were operating with strong runtime and infrastructure coverage and weak developer-workflow and remediation-routing coverage. They bought their way into it rather than building it, which is a reasonable strategic choice, but integration depth matters more than press-release proximity.
On the ASPM side, vendors are adding cloud context in the opposite direction. Cycode has cloud workload context capabilities. Ox Security correlates pipeline findings with deployed artifact status. The movement is bidirectional: ASPM vendors adding runtime awareness, CNAPP vendors adding pre-deployment pipeline coverage. Neither has fully closed the gap on the other’s core strength.
The practical consequence for buyers: an acquired capability in a unified platform is not the same as a purpose-built one. If your engineering organization runs a complex multi-scanner setup with custom routing rules and SLA tracking by team, a CNAPP’s remediation module that shipped eighteen months after an acquisition is unlikely to match the depth of a dedicated ASPM platform. If your organization is earlier-stage and primarily needs cloud workload visibility with basic pipeline scanning, the CNAPP’s added coverage may be sufficient without another vendor relationship.
Where Coverage Actually Overlaps and Where It Does Not
| Capability | CNAPP Coverage | ASPM Coverage | Notes |
|---|---|---|---|
| Cloud misconfiguration detection (CSPM) | Core capability | Partial, via integrations | ASPM typically ingests CSPM findings rather than generating them |
| Container image scanning | Core capability | Via scanner integrations | CNAPP has registry and runtime context; ASPM normalizes findings |
| SAST findings management | Partial, post-acquisition | Core capability | ASPM connects to multiple SAST tools; CNAPP often supports one or two |
| SCA and open source risk | Partial | Core capability | ASPM typically has broader SCA scanner support |
| Secrets detection in code | Partial, via pipeline integrations | Core capability for dedicated vendors | Varies significantly by vendor |
| CI/CD pipeline security | Partial, post-acquisition (Cider, Dazz) | Core for most ASPM vendors | CNAPP pipeline coverage depends heavily on integration maturity |
| Developer ticket routing | Limited | Core capability | ASPM owns Jira/ADO/GitHub Issues integration depth |
| Attack path analysis (cloud) | Core capability | Absent or shallow | CNAPP maps lateral movement paths through deployed infrastructure |
| Runtime workload behavior | Core capability | Absent | ASPM has no runtime sensor |
| Internet exposure context | Core capability | Absent | Critical for prioritization; ASPM relies on CNAPP to supply this |
| SBOM generation and tracking | Partial | Core for mature ASPM vendors | ASPM vendors typically produce and manage SBOMs across pipelines |
| Remediation SLA tracking by team | Limited | Core capability | ASPM tracks fix velocity; CNAPP typically reports open finding counts |
The SecurityOpsWire Code-to-Cloud Coverage Audit: Eight Questions Before You Consolidate
Most consolidation conversations start with the procurement question: can we reduce vendors? That is a legitimate goal. The better question is which coverage gaps become accepted risks once you do. The following eight questions, run before you sign either a CNAPP expansion contract or a standalone ASPM contract, surface the gaps most teams discover six months post-deployment.
- How many SAST and SCA scanners does your engineering organization currently run? If the answer is more than two, a CNAPP’s built-in scanner will not cover all of them. Findings from unsupported scanners disappear from the consolidated view unless the CNAPP has an open ingestion API with field mapping support.
- Does your engineering org have clear code ownership mapped to services? Developer-routing only works if the platform knows who owns what. ASPM platforms typically build or import ownership maps. CNAPP platforms usually route by cloud resource tag, which works for infrastructure owners but not always for application developers.
- Do you need to track remediation SLAs by engineering team? If the answer is yes, check whether your CNAPP produces per-team SLA reports out of the box. Most do not. This is where ASPM platforms typically outperform.
- Are your highest-risk applications deployed on cloud infrastructure the CNAPP can see? CNAPP runtime context is only useful for workloads running on supported cloud platforms. On-prem workloads or third-party-hosted services are usually invisible to the CNAPP’s runtime layer.
- Do you have a software supply chain compliance requirement that requires SBOM delivery? Check which platform actually generates, tracks, and exports SBOMs in the format your compliance framework requires. This is not a feature all platforms have at the same depth.
- What is the primary consumer of vulnerability findings: the security team or engineering teams? If engineering teams consume findings directly, developer-experience tooling matters. ASPM platforms are built for developer consumption. CNAPP platforms are built for security team consumption.
- Do you need to correlate pre-production findings with runtime exposure? If yes, you need both layers, either from one platform that genuinely integrates them or from two platforms that share data via API. Ask the CNAPP vendor to demonstrate a specific finding that connects a code-level vulnerability to a live, internet-exposed workload path.
- What does your cloud environment look like in three years? A team moving from a hybrid on-prem posture to cloud-native over two years will find CNAPP coverage increasing naturally as the migration progresses. A team with permanent on-prem or edge workloads will always have a CNAPP blind spot on those workloads.
Which Platform Should Own Application Risk in Practice?
The ownership question depends on where your application risk actually lives and who in your organization needs to act on it. There is no universal answer, but there are clear environmental signals.
CNAPP as primary, ASPM supplemental: cloud-native engineering orgs with small security teams
If your engineering organization is cloud-native, runs containerized workloads, and your security team is small relative to your developer count, CNAPP as the primary platform makes operational sense. The runtime context for prioritization is where most of your risk lives. A security team of two or three people cannot manually route findings to developers anyway, so the sophistication of ASPM’s developer-workflow layer is partially theoretical until you have the headcount to operate it. The CNAPP’s consolidated view reduces the number of systems a small team has to monitor. Accept that you will have shallower coverage of pre-deployment pipeline findings and manage that gap explicitly.
ASPM as primary, CNAPP data fed in: mature engineering orgs with large developer populations
If your engineering organization has ten or more engineering teams, each owning distinct services, and your security program already runs multiple scanners, ASPM as the primary application risk platform makes more sense. The core problem at scale is not finding vulnerabilities: the scanners already find them. The problem is normalization, deduplication, prioritization, and routing. That is exactly what ASPM is built to do. The CNAPP still belongs in the stack for cloud infrastructure and runtime coverage, but it feeds data into the ASPM’s risk model rather than owning the application risk view. Vendors like ArmorCode and Cycode support CNAPP finding ingestion explicitly for this pattern.
Integrated CNAPP with acquired ASPM capabilities: mid-market teams optimizing for vendor count
For mid-market security programs that genuinely cannot justify two enterprise platform contracts, the CNAPP’s acquired application security capabilities may be sufficient. The honest assessment of this path: you will get 70 to 80 percent of what a dedicated ASPM delivers, with gaps concentrated in multi-scanner normalization, developer ticket routing depth, and SBOM management. Whether that gap matters depends on your compliance requirements and your developer organization’s maturity. It is a reasonable trade. Name it explicitly in your program documentation rather than discovering it during an audit.
For cloud-native teams trying to understand where application security tooling fits alongside their cloud security posture work, the broader question of ASPM tools for cloud-native environments is worth mapping before a consolidation decision.
What Coverage Is Actually Lost When You Consolidate Into CNAPP?
The coverage losses from consolidating into CNAPP are predictable. Teams rarely lose them because they made a bad decision. They lose them because the vendor’s demonstration did not surface the gap, and internal stakeholders assumed “code to cloud” meant full coverage on both ends.
The most common losses, in order of how often they surface post-consolidation:
- Multi-scanner normalization: findings from scanners the CNAPP does not natively support disappear unless the team builds and maintains custom ingestion pipelines. Security engineering time spent maintaining those pipelines is often invisible until someone leaves the team.
- Developer-routed remediation: CNAPP platforms route findings to cloud resource owners, not code owners. In organizations where the cloud resource owner and the code owner are the same person, this does not matter. In organizations with a platform engineering team that owns infrastructure separately from application developers, tickets go to the wrong place and age out without action.
- Scanner breadth: CNAPP built-in SAST typically covers major languages well and less common languages poorly. If your engineering organization runs services in Go, Rust, or less common frameworks, verify scanner coverage before assuming it exists.
- SBOM generation and lifecycle management: most CNAPP platforms can generate an SBOM from a container image or a deployed artifact. Managing SBOM versions across multiple services, tracking component changes across releases, and producing VEX documents for downstream consumers is a different capability. Dedicated ASPM and supply-chain security platforms typically handle this more completely.
- Remediation velocity tracking: security programs that report fix rates to the board need per-team, per-severity SLA metrics. CNAPP platforms typically report vulnerability counts and age. ASPM platforms typically report remediation velocity by team, which is the metric that actually tells you whether your program is working.
Software supply chain risk compounds all of these gaps. Teams managing dependency risk across a large engineering organization will find the dedicated software supply chain security platforms more complete than what either CNAPP or ASPM vendors have built into their core products.
Does Consolidating Into CNAPP Actually Cost Less?
The consolidation-saves-money assumption deserves examination. CNAPP platforms do not publicly publish pricing, and neither do most ASPM vendors. Both categories price based on environment size, workload count, developer seats, or data volume depending on the vendor. Quotes vary significantly by negotiation.
The honest consolidation math includes costs that vendor proposals do not show. When a team drops a dedicated ASPM to run on CNAPP’s application security module, they typically spend engineering time rebuilding the integrations that the ASPM handled natively: scanner ingestion pipelines, Jira field mappings, code ownership imports, SLA threshold configurations. That time has a cost. In a team of three security engineers, a four-to-six-week re-integration project is not a line item in the consolidation analysis, but it is real.
The genuine cost savings from consolidation are in reduced vendor management overhead, unified identity and access administration, and consolidated data residency. Those are real, particularly for security programs that have accumulated five or more point tools and are paying per-seat licensing on each. Consolidation makes the most financial sense when the tools being retired have low utilization or significant feature overlap with the surviving platform. It makes the least sense when the retired tool is deeply integrated into engineering workflows that will have to be rebuilt from scratch.
Teams evaluating how exposure management and vulnerability prioritization fit into this picture should consider how the application vulnerability prioritization layer changes when the platform providing runtime context also owns the scanner output.
How Do CNAPP Vendors Address Application Security Credibility?
The major CNAPP vendors have made different bets on how to close the application security gap. Wiz acquired Dazz for remediation context and developer routing. Palo Alto Networks Prisma Cloud absorbed Cider Security for pipeline and supply chain coverage. Orca Security focuses on agentless cloud coverage with code-to-cloud context but positions more at the infrastructure risk layer than at developer-workflow depth. Fidelis Cybersecurity has a different product architecture oriented more toward network detection and endpoint, with cloud coverage that does not put it in the same CNAPP conversation as Wiz or Prisma.
The ASPM vendor responses are equally instructive. Cycode built a platform that explicitly ingests CNAPP findings alongside scanner output, positioning itself as the normalization and correlation layer above both. ArmorCode similarly aggregates findings from CNAPP platforms. Ox Security emphasizes pipeline integrity and supply chain attack detection as its differentiator.
No vendor has a fully honest “code to cloud” story yet without gaps. The acquisitions are moving both categories closer together, but integration maturity lags acquisition completion by a year or more in most cases. Evaluating the acquired capability requires asking specifically which features were available before the acquisition and which were added after, then asking for a reference customer running the post-acquisition integration in production.
Frequently Asked Questions
What is CNAPP in cybersecurity?
CNAPP, or Cloud Native Application Protection Platform, is a category of security platform that consolidates cloud security posture management (CSPM), cloud workload protection (CWPP), cloud infrastructure entitlement management (CIEM), and increasingly CI/CD pipeline scanning into a single platform. It is designed to give security teams a unified view of risk across cloud-deployed infrastructure, from misconfigured storage buckets to vulnerable container images to overprivileged service accounts. Gartner coined the category name. Wiz, Palo Alto Prisma Cloud, and Orca Security are among the commonly cited platforms.
Is ASPM just another name for a vulnerability management platform?
No. Traditional vulnerability management platforms track CVEs across infrastructure and endpoints. ASPM is specifically focused on application security findings generated by developer-side tools: SAST, DAST, SCA, secrets scanners, and CI/CD pipeline analyzers. Its distinguishing function is normalizing output from multiple scanners into a single risk view and routing findings to the engineering teams responsible for fixing them. Vulnerability management platforms typically do not have code ownership mapping or developer-ticket integration at the depth ASPM platforms do.
Can a CNAPP replace a dedicated ASPM platform?
For some organizations, yes. For others, no. A CNAPP can replace ASPM when the engineering organization is cloud-native, the security team is small, and scanner breadth requirements are modest. It cannot replace ASPM when the organization runs more than two or three scanner tools, has complex code ownership across many teams, needs per-team SLA tracking for remediation, or has software supply chain compliance requirements that demand SBOM lifecycle management. The acquisitions CNAPP vendors have made to close this gap add capability, but integration maturity takes time.
What does “code to cloud” actually mean in CNAPP marketing?
“Code to cloud” means the platform covers application risk from the development pipeline through to the deployed cloud workload. In practice, CNAPP platforms do this better at the cloud end than the code end. The strongest CNAPP code coverage is typically container image scanning, pipeline CI/CD integration, and IaC misconfiguration detection. The weakest areas are SAST finding management, multi-scanner normalization, and developer-workflow ticket routing. Evaluating a vendor’s “code to cloud” claim requires asking for a live demonstration of a finding that traces from a code commit through to a cloud runtime risk, with developer routing, not just a slide.
Which ASPM vendors support CNAPP finding ingestion?
Several ASPM platforms are designed to ingest findings from CNAPP platforms as one of many scanner sources, treating the CNAPP as a cloud security data feed rather than a competitor. Cycode and ArmorCode both support this pattern. The practical value is that teams running both platforms can use the ASPM as the normalization and prioritization layer across all finding sources, including the CNAPP, giving developers a single interface for all security findings regardless of origin. This is a reasonable architecture for larger engineering organizations with complex multi-team ownership.
Does software supply chain security belong in CNAPP or ASPM?
Supply chain security spans both categories and fits neatly in neither. Pipeline integrity monitoring, dependency review in CI, and secrets detection in code belong more naturally in the ASPM layer. Container image provenance, registry scanning, and runtime artifact verification belong more naturally in the CNAPP layer. SBOM generation and lifecycle management is a functional gap in both categories; dedicated software supply chain platforms like those from Snyk or Chainguard cover it more completely. For teams with regulatory SBOM requirements, neither CNAPP nor ASPM should be assumed sufficient without verification.
What coverage is typically lost when consolidating AppSec into a CNAPP?
The most common coverage losses after CNAPP consolidation are: multi-scanner normalization for tools the CNAPP does not natively support, developer-oriented ticket routing based on code ownership rather than cloud resource ownership, SBOM lifecycle management, remediation SLA tracking by engineering team, and SAST coverage for less common programming languages. These gaps are predictable and manageable if they are named explicitly at the time of consolidation. They become problems when they are discovered during a compliance audit or a post-incident review.
How should security leaders frame the ASPM vs CNAPP decision for the board?
Frame it as a scope question, not a technology question. Ask the board: do we want visibility into application risk in our cloud environment, or do we want visibility into application risk across our entire development lifecycle? CNAPP answers the first question well. ASPM answers the second. The honest board-level framing for consolidation is: we are accepting shallower developer-workflow coverage in exchange for fewer vendor contracts and a simpler security architecture. Name the trade explicitly. Boards that approved consolidation based on cost savings and later discovered coverage gaps are not well-served by a technology answer that obscured the scope decision.
The Coverage Map Is the Decision
The ASPM versus CNAPP question resolves most cleanly when teams stop asking “which platform is better” and start asking “which risks am I accepting with each architecture.” CNAPP platforms are genuinely strong at cloud runtime risk: they see the deployed environment, they trace attack paths through cloud infrastructure, and they provide the runtime context that makes vulnerability prioritization meaningful rather than theoretical. That is valuable, and for teams whose primary exposure is in cloud-deployed workloads, it is often sufficient.
The gap is upstream. Developer workflows, multi-scanner normalization, code ownership routing, and SBOM lifecycle management are where purpose-built ASPM platforms have depth that CNAPP vendors are still building toward through acquisitions. The Wiz-Dazz and Palo Alto-Cider moves accelerate that convergence, but the right question for any evaluation is not whether an acquisition happened but whether the integration is production-mature in an environment similar to yours.
Run the eight-question coverage audit before the contract negotiation, not after. The vendor whose platform wins the consolidation decision will shape how your organization sees application risk for the next three years. Getting the scope of that visibility right at the start is worth more than any discount negotiated at the end of a quarter. If you are navigating related prioritization questions at the intersection of AI-generated code and application security posture, the considerations around ASPM platforms for AI-generated code add a layer that neither CNAPP vendors nor traditional ASPM vendors have fully answered yet.