TLDR
- SOAR and AI SOC tools fail in different directions: SOAR breaks when an alert falls outside a written playbook, while an AI SOC agent can hallucinate or take unvalidated action when the reasoning chain is wrong.
- The core architectural difference is decision location. SOAR executes predetermined branches. An AI SOC agent decides what to investigate, what evidence to pull, and what conclusion to draw before any branch is executed.
- Most teams that adopt an AI SOC layer end up keeping SOAR for response actions, approvals, and ticketing integrations, because those workflows require deterministic audit trails that LLM-based systems do not reliably produce.
- Three-year maintenance cost is where playbook-based automation usually loses: tuning debt compounds faster than most teams budget for, while AI SOC tools shift the cost to prompt engineering and model validation instead.
- The right architecture for most mid-to-enterprise teams is a thin SOAR layer below an AI decisioning layer, not a replacement of one with the other.
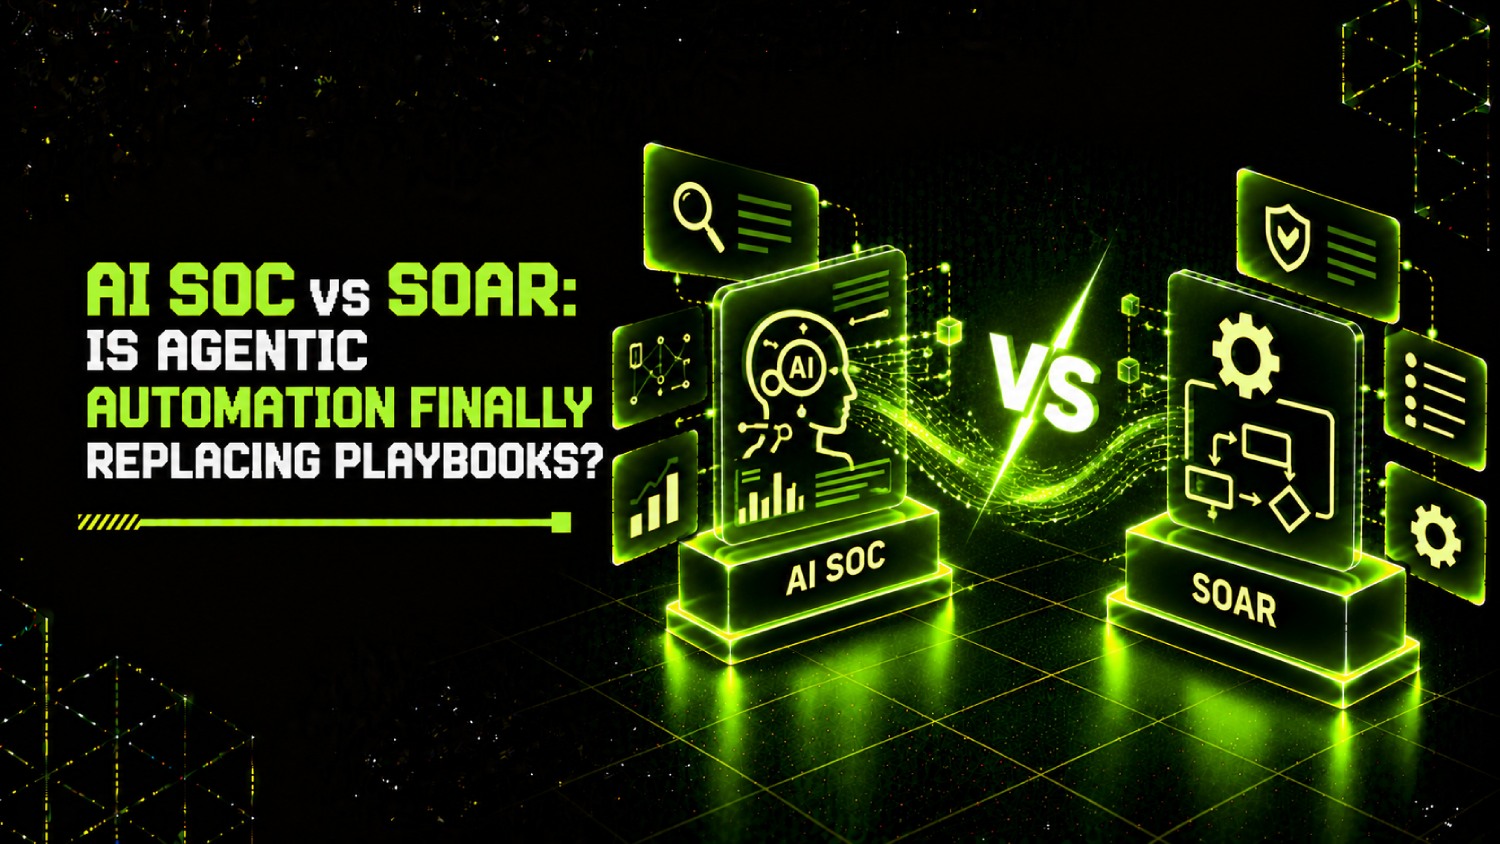
SOAR executes the workflow your team wrote in advance. An AI SOC agent reads the alert, decides what to investigate, gathers evidence autonomously, and delivers a verdict before any playbook fires. They solve different problems at different points in the triage chain, and most teams that remove SOAR entirely discover they need to rebuild its response-action and approval logic inside a tool that was not designed for it. Understanding the AI SOC vs SOAR distinction is the starting point for any architecture decision in this space.
Why Did SOAR Playbooks Fail to Scale in the First Place?
Playbook debt is the real answer. Every SOAR deployment starts with a manageable library of workflows: enrich this IP, disable this account, open a ticket, page the on-call analyst. The first dozen playbooks take a week to build and work well. Then the environment changes, a new detection rule fires on a slightly different alert structure, and the playbook breaks silently. Someone writes a new playbook instead of fixing the old one. After eighteen months, a mid-sized SOC team is maintaining eighty-plus playbooks, a third of which are partially broken, and no one knows which third.
The structural problem is that a playbook is a decision tree written at a specific moment in time, against a specific understanding of the environment. SOAR does not rewrite that tree when the environment changes. The analyst does, manually, when they notice something misfired. Detection engineering teams use the phrase tuning debt to describe the accumulated cost of detection logic that has drifted from the environment it was written for. Playbooks accumulate the same kind of debt, but it is harder to see because a broken playbook often appears to complete successfully while skipping branches that should have fired.
Alert volume is the second problem. SOAR reduced analyst load on the workflows it covered, but it did not reduce the total number of alerts arriving in the queue. As cloud telemetry, identity signals, and third-party tool integrations multiplied the raw event volume, the percentage of alerts with a matching playbook stayed roughly the same or shrank. Analysts still handled every out-of-playbook alert manually, which is exactly the triage work that takes the most time.
What Does Agentic Automation Actually Do Differently From a Playbook?
A playbook is a state machine. It moves from state A to state B based on a condition your team specified at authoring time. An AI SOC agent is closer to an investigator: it reads an alert, forms a hypothesis about what might have happened, queries logs and context to test that hypothesis, and produces a structured finding with supporting evidence. The decision of what to investigate is made at runtime, not at authoring time.
The practical consequence is that an AI SOC agent can handle alert types it has never seen a specific playbook for, as long as it has access to the right data sources and a general understanding of what constitutes suspicious behavior in that environment. A SOAR platform presented with an unfamiliar alert either drops it to a manual queue or misroutes it through the closest matching playbook, neither of which is investigation.
The failure modes are different, and that matters. SOAR fails predictably: the playbook either has no matching condition or it executes the wrong branch. The failure is usually visible and auditable. AI SOC agents fail probabilistically: the reasoning chain is plausible but wrong, the agent queries the right sources but draws an incorrect conclusion, or it escalates with high confidence on a benign event because context it needed was not accessible. Vendors including Dropzone AI position their agents as delivering evidence-backed verdicts precisely to address this confidence problem, but the quality of the verdict is still bounded by what the agent can reach and reason over. If you are evaluating how to assess those bounds systematically, the SecurityOpsWire analysis of AI SOC analyst tools for Tier-1 alert investigation covers how different platforms handle evidence gathering and confidence scoring.
The SOC Automation Layer Cake: Where Each Tool Actually Sits
Framing this as a replacement decision misses the operational reality. The more useful mental model is a stack with three layers.
Layer one: signal and detection
Your SIEM, EDR, and cloud telemetry generate alerts. Nothing in this layer is being displaced by the SOAR-versus-AI-SOC question.
Layer two: investigation and decisioning
This is where an AI SOC agent operates. It receives an alert, gathers context, and produces a verdict: close as false positive, escalate as confirmed incident, or flag for human review with evidence attached. This layer did not exist in most SOAR deployments. SOAR was called to this layer but was never designed for it. Playbooks route and enrich; they do not reason.
Layer three: response execution
Blocking an IP, disabling an account, isolating an endpoint, opening a P1 ticket, paging an on-call engineer. This is what SOAR does well and what most teams should keep SOAR for. These actions need deterministic logic, approval gates, and audit trails. An AI agent executing a block action autonomously, with no human approval step and no deterministic audit log, is a governance and compliance risk that most enterprise security teams cannot accept.
The architecture that works in practice is: AI SOC agent in layer two, SOAR in layer three. The agent hands a verdict and a recommended action to SOAR, which executes the response workflow with its existing connectors, approval logic, and ticketing integrations. Neither tool is wasted.
What Does SOAR Still Do Better Than an AI SOC Agent?
Three things, and each matters enough to keep a SOAR contract for.
Deterministic response actions with approval gates. When an analyst needs to approve an account disable before it fires, or when a response action requires a change-management ticket before execution, SOAR handles this through structured conditional logic. An AI agent can recommend the action, but the approval workflow requires the kind of explicit branching and role-based gate that playbook systems were built for. Vendors like D3 Security and Torq have built significant integration libraries around exactly this use case.
Ticketing and case management integrations. SOAR platforms typically ship with pre-built integrations to ServiceNow, Jira, PagerDuty, and similar systems, with field-mapping, bidirectional updates, and SLA tracking. AI SOC platforms are adding these integrations, but the depth and reliability of a mature SOAR ticketing integration is not yet matched by most AI-first tools. This is a maintenance-cost consideration: if you rip out SOAR and lose those integrations, someone rebuilds them.
Audit trails for regulated environments. If you are in a regulated industry where every response action must be logged with a timestamp, an operator identity, and an approval record, the deterministic execution model of SOAR produces cleaner evidence for compliance reviews than an LLM reasoning chain. That reasoning chain may be thorough, but it is harder to present to an auditor than a structured workflow log.
The SecurityOpsWire Three-Year Maintenance Cost Framework
Year-one cost comparisons between SOAR and AI SOC tools are almost meaningless. The divergence happens in years two and three, and almost no vendor comparison surfaces it. Below is a framework for mapping the real cost over a three-year horizon. Treat it as a planning model, not a budget figure, because both categories vary significantly by vendor and environment size.
| Cost Category | SOAR (Playbook-Based) | AI SOC Agent Layer |
|---|---|---|
| Year 1 implementation | High. Playbook authoring requires dedicated analyst time, often 3-6 months to reach meaningful coverage. | Moderate. Integration and data-source connection is the main lift. Prompts and confidence thresholds require tuning. |
| Year 2 tuning debt | High and growing. Each new detection rule or environment change may require playbook updates. Broken playbooks accumulate. | Lower. The agent adapts to new alert types without a new playbook, but model behavior must be monitored for drift. |
| Year 3 maintenance headcount | One to two dedicated engineers for a mature playbook library covering 60-plus workflows in a mid-market environment. | Closer to a part-time senior analyst responsibility, focused on reviewing verdicts and adjusting thresholds. |
| Failure mode cost | Silent playbook failure can let alerts age in a queue undetected. Discovery often happens post-incident. | False-confidence verdicts can close alerts that should escalate. Requires sampling and review discipline. |
| Integration rebuild risk | Low once built. Connectors are stable. | Moderate. Response-action integrations in AI SOC platforms are still maturing. Migration risk if you eliminate SOAR entirely. |
| Licensing model | Most vendors price per workflow execution, per user, or per year at a flat platform fee. Public pricing is not broadly disclosed. | Most vendors price per alert volume, per analyst seat, or as a platform fee. Public pricing is similarly limited. |
The practical finding from this model: teams that replace SOAR entirely with an AI SOC platform usually spend the second year rebuilding response-action logic and approval workflows in a tool not designed for them. Teams that add an AI SOC layer above their existing SOAR deployment see faster time-to-value because they are not migrating connectors. The upgrade path, not the replacement path, is cheaper over three years for any team with more than forty active playbooks.
Is SOAR Still Needed for Response Actions, or Can AI Agents Handle Them?
AI agents can technically execute response actions. Several AI SOC platforms have built direct API integrations to execute blocks, quarantines, and disables without routing through a SOAR layer. For small security teams without an existing SOAR investment, this is a reasonable architecture. For teams with existing SOAR deployments, mature playbooks, and compliance requirements around approval logging, it is a sideways move with significant migration cost and reduced auditability during the transition.
The more honest answer is that it depends on what response actions you are executing. Low-risk, high-volume, fully automated responses like closing a known-good alert, enriching a ticket with VirusTotal results, or updating a watchlist entry are fine for an AI agent to execute without SOAR in the middle. High-risk response actions like account disables, firewall rule changes, or endpoint isolation in a production environment warrant the approval gate and audit trail that SOAR provides, regardless of how confident the AI verdict is. Separating those two classes of action and routing them appropriately is the operational discipline that most teams skip when they design this architecture in a hurry.
If you are working through how to govern AI agent actions more broadly, the SecurityOpsWire coverage of AI guardrail platforms for production LLMs and AI agents is relevant context for what control surfaces exist between an agent and a live action.
A Worked Scenario: Mid-Market SOC, Two Engineers, Mixed Environment
The following scenario is illustrative. The company, team size, and alert figures are hypothetical, constructed to make the architectural tradeoffs concrete.
Consider a company with 600 employees, running two AWS accounts and an on-premise Active Directory environment, with a two-person security team and a SIEM ingesting roughly 120GB of logs per day. They have a SOAR deployment with thirty-two playbooks, built over two years, covering phishing triage, failed-login lockout, and basic IOC enrichment. Alert volume averages 400 alerts per day. The team handles maybe sixty of those manually; the rest close via playbook or age out.
In this environment, adding an AI SOC agent in the investigation layer would reduce the sixty manual alerts substantially, covering the alert types that fall outside existing playbooks. The AI agent would investigate, gather evidence from the SIEM and identity provider, and deliver a verdict. The SOAR layer would remain, handling the lockout and enrichment workflows the team spent two years building and trusting. The team does not rebuild thirty-two playbooks. They add a new tier above them and free up analyst hours for detection engineering and threat hunting.
Replacing SOAR entirely in this scenario would mean migrating thirty-two playbooks, rebuilding the Active Directory lockout connector, and losing the approval gate on account disables, which the team’s compliance framework requires. The time cost alone, at two-person capacity, is realistically a quarter of engineering time for six months. That is not a replacement project. That is a migration project disguised as an upgrade.
Which Teams Should Prioritize SOAR Replacement Versus SOAR Extension?
Teams with fewer than fifteen active playbooks and no existing SOAR contract are reasonable candidates for an AI SOC platform that handles both investigation and response. There is no playbook library to protect, no connector migration, and the operational simplicity of one tool handling both layers is real. Vendors purpose-built for this entry point exist, though the two named in an earlier draft of this article , Prophet Security and Secure.ai , could not be independently verified from available sources at the time of publication. Prophet Security’s positioning could not be confirmed, and the Secure.ai domain currently shows no product information. Any vendor evaluation in this segment should start from a current market review rather than named recommendations here.
Teams with thirty-plus active playbooks, existing SIEM integrations wired through SOAR, and a regulated environment should treat SOAR as infrastructure, not as legacy. The playbooks are working capital. The connectors took months to build. The approval workflows satisfy audit requirements. The correct decision is to extend, not replace: put an AI SOC agent in the investigation layer, reduce manual triage load, and let SOAR do what it was designed for. The SecurityOpsWire roundup of AI SOC platforms covers which products are designed to sit above an existing SOAR layer versus which are designed as full replacements.
Teams somewhere in the middle, with fifteen to thirty playbooks and a non-critical SOAR deployment, should run the three-year maintenance cost model above before deciding. If playbook debt is already consuming more than one engineer-day per week in maintenance, the case for a clean shift strengthens. If the playbooks are stable and the team is mostly fighting triage volume, the extension model is less disruptive and cheaper.
How Should Security Teams Evaluate AI SOC Platforms Without Getting Burned by Agentic Marketing?
Four questions that separate real agentic capability from LLM-wrapped enrichment.
- What evidence does the agent gather autonomously, and what does it require a human to configure first? Some platforms marketed as AI SOC agents are enrichment pipelines with a summary layer on top. Real agentic behavior means the system decides what to query, not just executes a fixed set of queries in a smarter wrapper.
- How does the platform handle a verdict it is not confident in? A system that always produces a verdict, regardless of evidence quality, is dangerous. Ask to see how the platform represents low-confidence findings and what it does differently when evidence is ambiguous.
- What happens to response actions? Does the platform execute them, recommend them, or route them to another system? This tells you where the tool sits in the layer model and whether your SOAR connectors survive the evaluation.
- How is the system evaluated for accuracy, and by whom? Vendors will show you recall on a curated alert set. Ask for false-positive rate on real production alerts, and ask what the review cadence looks like after deployment. If the answer is “the model improves automatically,” ask what monitoring exists to detect when it improves in the wrong direction.
The broader question of how to evaluate AI agent platforms without being captured by marketing framing is covered in depth in the SecurityOpsWire guide to evaluating AI agent security platforms, which applies the same skepticism to the vendor claims in this category.
Frequently Asked Questions
What is the core difference between an AI SOC and a SOAR platform?
SOAR executes workflows your team wrote in advance, following predetermined branches based on conditions defined at authoring time. An AI SOC platform investigates alerts autonomously at runtime, deciding what evidence to gather and what conclusion to draw without a prewritten playbook for every scenario. SOAR handles response actions well. AI SOC platforms handle investigation and triage. The two layers are complementary more often than they are substitutes.
Why did SOAR playbooks fail to scale for most SOC teams?
Playbook debt compounds faster than most teams budget for. Every environment change, new detection rule, or integration update can break a playbook silently. After two or more years, a typical mid-market deployment has a significant portion of its playbook library in a degraded state that no one has time to audit. Alert volume growth also outpaced playbook coverage, leaving a large percentage of alerts without any automated handling, which defeated the original scaling argument.
Is SOAR still necessary if you deploy an AI SOC platform?
For most enterprise teams, yes. AI SOC platforms handle investigation and triage well, but response actions in regulated environments require deterministic execution, approval gates, and structured audit trails. SOAR provides all three. The practical architecture is an AI SOC agent handling decisioning above an existing SOAR layer that handles response execution. Teams with no existing SOAR investment and fewer than fifteen workflows are the exception where a single AI SOC platform handling both layers is workable.
What does agentic automation do differently from playbook automation?
Playbook automation follows a fixed decision tree. Agentic automation decides at runtime what to investigate, what data to query, and what conclusion the evidence supports. An agentic system handles alert types it has never seen a specific playbook for, as long as it has access to relevant data and a working reasoning model. The trade-off is predictability: playbooks fail in known ways, while agentic systems can fail confidently in ways that are harder to detect without sampling discipline.
Which is cheaper to maintain over three years, SOAR or an AI SOC platform?
SOAR accrues maintenance cost through playbook tuning debt, which grows with environment complexity and alert volume. AI SOC platforms shift the cost to model validation, confidence threshold management, and verdict sampling. For teams with large playbook libraries, SOAR maintenance is often the larger cost in years two and three. The cleanest path to lower three-year cost is usually extending an existing SOAR investment with an AI investigation layer rather than replacing SOAR entirely and migrating connectors.
Can an AI SOC agent replace Tier-1 SOC analysts?
Current AI SOC platforms can automate a meaningful portion of Tier-1 investigation work, particularly for high-volume, well-understood alert types like phishing triage, failed-login analysis, and IOC correlation. They do not replace the judgment required for novel incidents, multi-stage intrusions, or situations where the relevant context is in a system the agent cannot reach. The more accurate framing is that an AI SOC agent handles the repetitive portion of Tier-1 volume, which frees analysts for the work that requires judgment rather than pattern matching.
Does SOAR use AI?
Most major SOAR platforms have added AI features, typically for playbook recommendation, alert summarization, or enrichment assistance. These additions are not the same as agentic investigation. A SOAR platform with an AI summarization feature still executes a predetermined playbook for the underlying response. The AI component reduces analyst reading time on a ticket; it does not change the architecture of how the platform decides what to do.
What is a playbook in the context of agentic AI?
In traditional SOAR, a playbook is a predetermined workflow: a graph of conditions and actions written by a human analyst. In the context of agentic AI, the term is sometimes applied to structured instructions or constraints that guide what an agent is permitted to do, what tools it can call, and in what order. These are not the same thing. An agentic “playbook” is closer to a policy or a system prompt than to a SOAR workflow, and conflating the two terms obscures where the decisioning actually happens.
Where Does This Leave the SOAR Renewal Decision?
The renewal question is the wrong frame if it is treated as binary. The actual question is whether your SOAR investment is doing work that would be costly to migrate, and whether the layer above it, the investigation and triage layer, is adequately staffed. If the answer to both is yes, the move is to add an AI SOC capability above SOAR, not to replace it. If your SOAR deployment has fewer than twenty active playbooks and weak connector coverage, renewal is less defensible, because an AI SOC platform with response-action capabilities handles that scope without the playbook maintenance burden.
What the vendor-driven debate obscures is that the value SOAR delivers is not in the playbooks themselves. It is in the response integrations and the approval logic those playbooks sit inside. Those integrations took months to build. The approval gates satisfy audit requirements that do not disappear because the investigation layer got smarter. Migrating them is real work with real risk. Any vendor telling you the migration is simple has not done it in a production environment with legacy ticketing integrations and a compliance team reviewing the audit trail.
The cleaner mental model for a security leader evaluating this in a budget cycle: AI SOC agents shift the automation frontier from “what response do I execute?” to “what should I even be looking at?” That is a meaningful advancement, and it addresses a gap that SOAR was never designed to fill. Keeping SOAR for what it was designed for, and putting an AI investigator above it, is not a compromise. It is the architecture that reflects what each tool actually does well. Teams that treat it as a replacement decision will spend their second year rebuilding what they dismantled.